Beware Of Sql Injection
To understand this we first need to know what is SQL injection? SQL injection is a web security vulnerability that allows an attacker to interfere with the queries that an application makes to its database. It generally allows an attacker to view data that they are not normally able to retrieve.
This might include data belonging to other users, or any other data that the application itself is able to access. In many cases, an attacker can modify or delete this data, causing persistent changes to the application's content or behavior.
SQL injection attacks happen when an attacker uses a web form field or URL parameter to gain access to or manipulate your database. When you use standard Transact SQL it is easy to unknowingly insert rogue code into your query that could be used to change tables, get information and delete data.
To prevent this from happening always use parameterised queries, most web languages have this feature and it is easy to implement.
Related Article
Gaffar Market
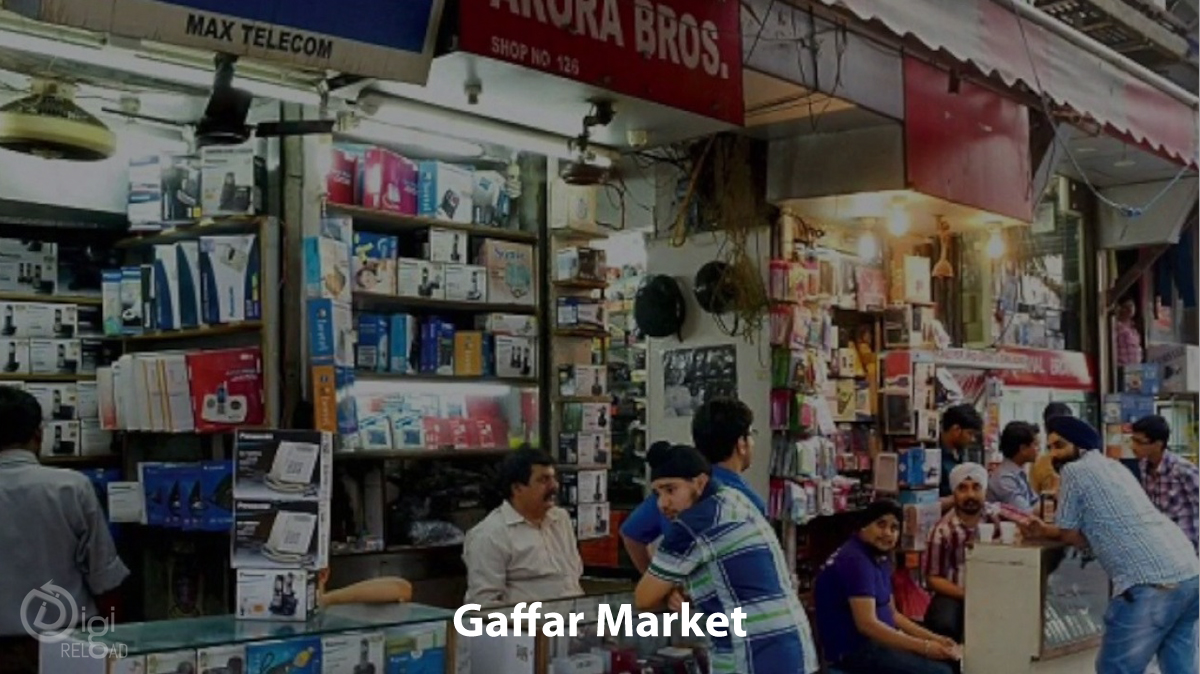
Gaffar market is a good market for personal electronics such as AC, TV, fridge, camera and mobile phones. Not only this, but you can also get your ...
Set up the WhatsApp Pay
Assuming you need to send and get installments by means of WhatsApp itself, here's the manner by which you can do it. Tap on the 3 dots or the ...

Build vocabulary
The people who have vast vocab & know-how to pronunciation are naturally considered as intelligent by others, because of their vocab knowledge ...
.png)